

Recent industry data confirms that 81% of organizations now actively partner with external specialists to architect their security frameworks. This shift represents a strategic response to the mandatory ISO 27001:2022 transition and the climate change requirements that became effective in 2024. For many executive leaders, the objective is no longer just a certificate; it’s securing ISO 27001 certification consulting that aligns information security with long-term digital transformation and organizational maturity.
Key Takeaways
- Understand how ISO 27001 functions as a global standard for organizational maturity and strategic digital transformation.
- Identify the critical criteria for selecting ISO 27001 certification consulting that prioritizes multidisciplinary vision over simple technical checklists.
- Distinguish between the data collection capabilities of automation software and the strategic governance provided by seasoned advisors.
- Master the essential roadmap of a premium engagement, from defining precise ISMS boundaries to executing robust risk treatment plans.
- Align your security framework with digital growth objectives to foster enhanced brand trust and operational excellence.
The Strategic Value of ISO 27001 Certification Consulting
ISO 27001 stands as the definitive global benchmark for Information Security Management Systems. It provides a structured framework designed to protect sensitive data while ensuring high levels of operational integrity and governance. Organizations often view this standard through a purely technical lens, yet its true power lies in its ability to align security protocols with broader commercial goals. Engaging in ISO 27001 certification consulting transforms this complex requirement from a defensive necessity into a proactive growth engine. By 2026, the transition to the ISO/IEC 27001:2022 version is a present mandate for all certified entities. Expert advisors bridge the gap between technical implementation and the strategic vision of the board, ensuring that every control serves a specific business outcome rather than existing in a vacuum.
A strategic partnership offers several key advantages that go beyond simple audit preparation:
- Market Differentiation: Certification acts as a powerful credential that accelerates sales cycles with enterprise clients who demand verified security.
- Strategic Alignment: Consulting ensures that security investments directly support the organization’s long-term stability and scalability.
- Risk Optimization: Professional guidance helps identify and prioritize risks that could impact the bottom line, rather than just technical vulnerabilities.
Why 2026 Demands a Strategic Approach to Security
The current threat landscape is characterized by increasing sophistication and relentless persistence. In Canada and across international markets, regulatory bodies have heightened their expectations for data sovereignty and privacy, making traditional security methods insufficient. Stakeholders now demand more than “checkbox compliance” which merely provides a veneer of safety; they seek verified proof of a mature security posture. A strategic approach ensures that your security framework directly supports your digital transformation strategy. This alignment allows for the secure adoption of emerging technologies, such as artificial intelligence and cloud-native architectures, without compromising the organization’s risk profile or operational continuity.
Beyond IT: The Executive Impact of a Robust ISMS
A well-implemented ISMS delivers tangible benefits that resonate far beyond the server room. It acts as a shield against legal liability and provides a compelling narrative for insurers, which can lead to more favorable terms and reduced premiums. When security is integrated into the corporate DNA, it strengthens organizational resilience by ensuring the business can withstand and recover from unforeseen disruptions. High-level ISO 27001 certification consulting empowers leadership to make informed decisions based on accurate risk data. An Information Security Management System is a living ecosystem of people, processes, and technology designed to manage risks and protect information through a cycle of continuous improvement.
Essential Criteria for Selecting an ISO 27001 Partner
Selecting a partner for ISO 27001 certification consulting requires a shift in perspective. Technical proficiency is merely the price of entry. The true differentiator lies in a partner’s ability to provide a multidisciplinary vision that harmonizes security with your organizational culture. A premium consultant doesn’t just implement controls; they architect a system that supports your commercial objectives. They must demonstrate a deep understanding of the ISO 27001 implementation roadmap while remaining flexible enough to adapt to your unique operational environment. Rigid, one-size-fits-all templates often fail because they don’t account for the specific nuances of your digital assets or existing workflows.
Effective consulting also involves the seamless integration of security with other established systems. If your organization already utilizes ISO 9001 for quality management, your partner should look for synergies between the two frameworks. This holistic approach prevents the creation of siloed processes and reduces the administrative burden on your team. Furthermore, a sophisticated advisor will be well-versed in global benchmarks such as NIST Special Publication 800-53. Citing these authoritative standards allows for a more robust mapping of security and privacy controls, ensuring your ISMS is both comprehensive and internationally recognized.
The “Big Firm Standards vs. Boutique Agility” Framework
Large consulting firms often leverage their global brand to win contracts but frequently assign “junior-heavy” teams to the actual execution. This can lead to a lack of depth and a reliance on generic solutions. In contrast, a boutique advisory offers the same high-level standards with significantly more agility. You gain direct access to senior-level mentors who provide customized roadmaps and dedicated attention. This ensures your ISO 27001 certification consulting experience is focused on high-impact results rather than billable hours. Senior architects understand how to transform complex compliance requirements into sustainable business advantages.
Audit Readiness and Third-Party Liaison
A consultant acts as a vital bridge between your organization and accredited registrars. Their role is to translate complex audit requirements into actionable steps for your staff. Verify your potential partner’s track record in identifying and resolving non-conformities long before the external auditor arrives. “Audit Simulation” workshops are particularly valuable in this phase. These sessions build internal confidence and prepare your team for the scrutiny of a formal assessment. This proactive preparation ensures a smoother certification journey and fosters a culture of transparency. If you’re ready to evaluate your current security posture, you can consult with a strategic advisor to begin the process.
Hiring a Consultant vs. Using Compliance Automation Software
The rise of SaaS-based compliance platforms has led some leadership teams to believe that certification is a purely technical exercise. These tools excel at data collection and continuous monitoring, yet they often lack the contextual intelligence required for high-level governance. Choosing ISO 27001 certification consulting ensures your Information Security Management System reflects your actual risk appetite rather than a generic template. While software can easily flag a missing policy or an unencrypted drive, a seasoned consultant defines how those controls integrate into your daily operations and broader digital transformation consulting efforts. This strategic oversight prevents the creation of a “paper-only” system that looks good on a screen but fails in a live audit environment.
A hybrid approach often yields the most effective results for modern enterprises. Technology streamlines the gathering of evidence and provides a central repository for documentation, but human experts remain the primary drivers of implementation. Adhering to the official ISO/IEC 27001:2022 standard requires more than just technical checks; it demands a comprehensive understanding of Clause 4 through Clause 10, which focus on organizational context and leadership commitment. Human-led guidance is indispensable for complex risk assessments where qualitative judgment outweighs quantitative data. Consultants provide the essential “how” and “why” behind each control, ensuring your team understands the logic of the framework they must maintain.
When Software Falls Short: The Human Element of Security
A “security-conscious culture” is an organic development that software cannot install. Algorithms are blind to the interpersonal dynamics, departmental silos, and legacy processes that define your organization’s unique DNA. Consultants handle these nuances by conducting deep-dive interviews, facilitating cross-functional workshops, and tailoring policies to the specific habits and constraints of your workforce. While SaaS platforms provide a visually appealing dashboard of status bars, they cannot navigate the strategic decision-making required to balance security with operational efficiency. A strategic partner mentors your team, transforming them into active participants in the security lifecycle.
Total Cost of Ownership (TCO) Analysis
Evaluating the investment in security requires looking beyond the initial invoice or subscription cost. Software platforms often carry recurring annual fees that accumulate significantly over a three-year certification cycle. Additionally, automated tools still require substantial internal staff time to configure, manage, and troubleshoot, which can lead to a hidden drain on your most valuable resources. ISO 27001 certification consulting provides a value-driven alternative focused on knowledge transfer and long-term self-sufficiency. By getting the architecture right the first time, organizations avoid the high cost of remedial work following a failed audit or a misconfigured control. The ROI of expert guidance is found in the creation of a lean, efficient system that minimizes disruption to daily workflows while maximizing protection.
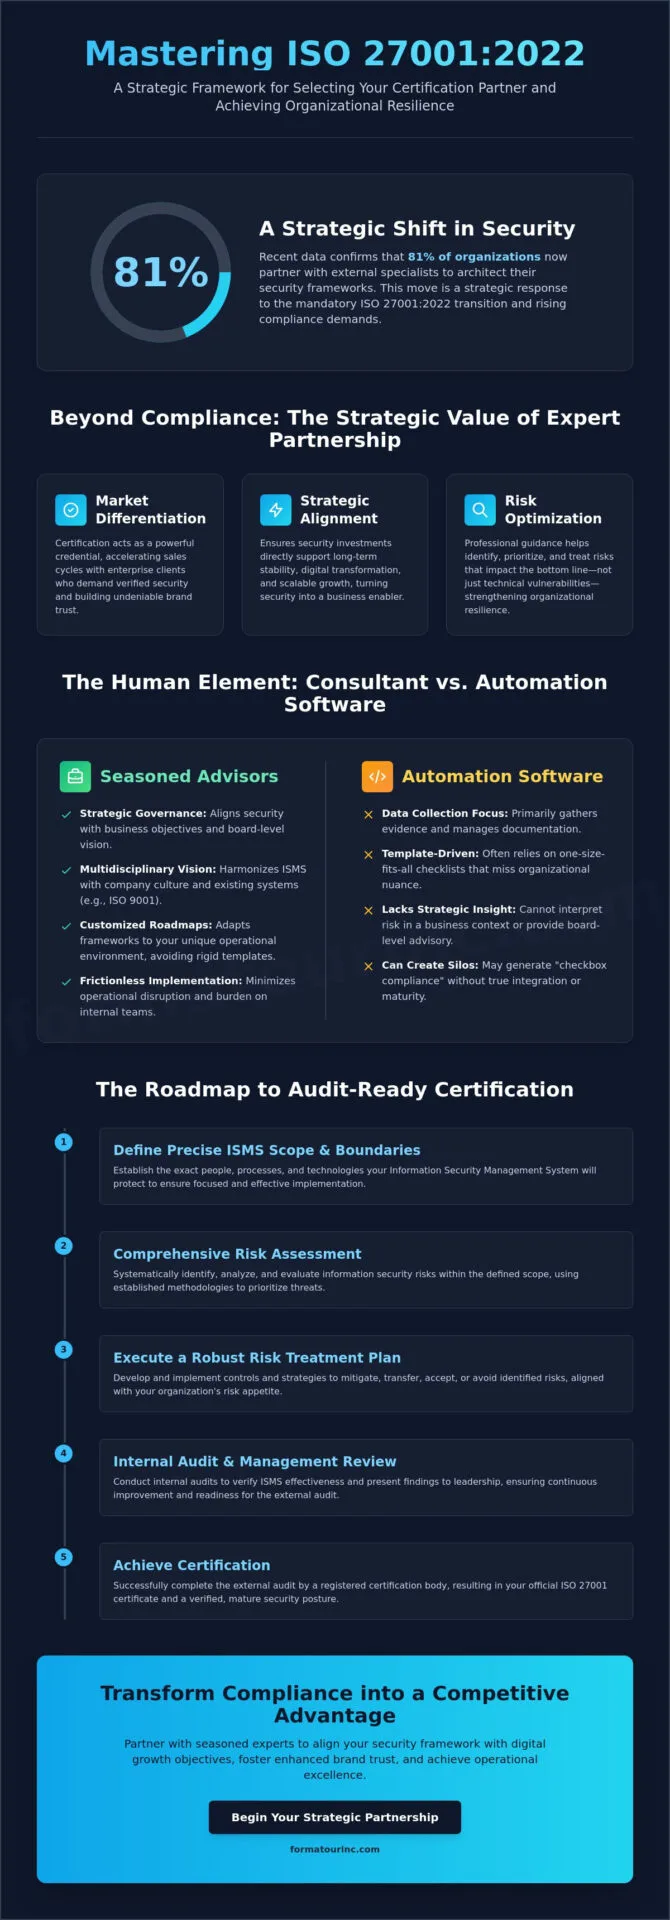
The Roadmap: What a Premium Consulting Engagement Looks Like
The subsequent phases focus on building a resilient and verifiable framework:
- Risk Assessment and Treatment: This is the core of the ISO 27001 philosophy. Advisors help you identify risks specific to your digital assets and determine whether to treat, transfer, tolerate, or terminate them based on your risk appetite.
- Documentation and Control Implementation: Consultants guide the creation of an evidence trail. Policies and procedures are drafted to reflect actual practice, ensuring the system is both compliant and functional for your daily workflows.
- Internal Audit and Management Review: Before the external registrar arrives, an internal audit acts as a vital stress test. This phase validates the system’s effectiveness and ensures that executive leadership is actively involved in the review process.
- Certification Audit Support: Your partner serves as a strategic liaison during the Stage 1 and Stage 2 external audits, providing the confidence and technical support needed to clear the final hurdle.
Empowering Your Internal Teams
Long-term success requires more than just expert guidance; it demands internal competence. Investing in ISO 27001 lead auditor training for your staff ensures the ISMS remains sustainable post-certification. This technical empowerment is often paired with Executive Leadership Development Programs to secure top-down support for security initiatives. When knowledge transfer is prioritized, your organization becomes self-reliant, viewing security as a strategic pillar rather than a temporary project.
The Continuous Improvement Cycle
ISO 27001 is not a “once-and-done” achievement. It’s a commitment to ongoing optimization throughout a three-year certification cycle. Annual surveillance audits verify that your controls remain effective as your business scales. Many organizations utilize vCISO services to provide steady, expert oversight without the overhead of a full-time executive hire. This continuous engagement ensures that your ISO 27001 certification consulting investment delivers value long after the initial certificate is issued. Connect with a strategic mentor to begin your roadmap today.
Why Formatour is the Strategic Choice for ISO 27001 Excellence
Formatour delivers the rigorous standards expected of a global firm while maintaining the personalized agility of a boutique advisory. This balance is critical for organizations that require deep expertise without the bureaucracy of traditional large-scale consultancies. Our ISO 27001 certification consulting methodology is built on the belief that security shouldn’t be a siloed IT project. Instead, it must be an integrated component of your operational performance and digital growth. We don’t just act as technical auditors; we serve as seasoned strategic mentors who help you navigate the complexities of governance and risk management with precision. Recent data indicates that 81% of organizations now actively seek external partnerships to manage these complexities, making the choice of a multidisciplinary advisor more vital than ever.
Our team specializes in executing the 2026 strategic roadmap to compliance. This expertise ensures your organization is prepared for the specific challenges of the current regulatory environment, including the 2024 climate change amendments and the strict requirements of the 2022 standard. By focusing on the co-development of solutions, we ensure that the resulting ISMS is practical, sustainable, and tailored to your unique business context. We prioritize the transformation of your internal processes, ensuring that compliance becomes a natural extension of your daily workflows rather than a disruptive burden.
A Holistic Advisory Ecosystem
Success in modern governance requires a unified perspective that connects various pillars of organizational health. Formatour enables you to integrate ISO 27001 with other critical frameworks such as ISO 9001 for quality, ISO 22301 for business continuity, and ISO 14001 for environmental management. This multidisciplinary approach creates a cohesive management system that reduces redundancy and enhances structural integrity across the enterprise. Our Canadian heritage provides a grounded, reliable foundation, while our global perspective ensures you meet international benchmarks with ease. We also leverage our background in executive education to foster a culture of excellence, empowering your leadership to champion security as a core business value.
Ready to Transform Your Security Posture?
A partnership with Formatour is founded on trust, precision, and a shared vision for your future success. We provide the steady hand needed to guide you through complex organizational landscapes, ensuring your digital assets remain secure and your brand trust continues to grow. We focus on long-term impact and sustainable development, moving beyond superficial fixes to build a robust, audit-ready framework. If you’re seeking a partner dedicated to collaborative success and strategic foresight, we invite you to begin your journey today. Partner with Formatour for your ISO 27001 journey and secure your organization’s strategic advantage.
Secure Your Digital Future Through Strategic Governance
Achieving excellence in information security requires a shift from viewing compliance as a hurdle to recognizing it as a strategic catalyst. By prioritizing a multidisciplinary approach, organizations transform their security posture into a verified asset that accelerates growth and builds enduring brand trust. Selecting the right ISO 27001 certification consulting partner ensures that your management system remains agile, sustainable, and perfectly aligned with your long-term digital objectives.
Formatour brings over a decade of multidisciplinary advisory experience to your organization. As a Canadian firm operating with global consulting standards, we specialize in the seamless integration of ISO 9001, 27001, 22301, and 14001 frameworks. Our seasoned mentors are dedicated to your collaborative success, providing the steady hand needed to navigate complex global benchmarks. We empower your leadership and internal teams to build a resilient ecosystem that thrives in the face of evolving risks.
Secure Your Strategic Advantage – Book an ISO 27001 Consultation
Your journey toward a more secure and resilient future begins with a single, decisive step. We’re ready to help you architect a system that protects your assets today and scales with your vision for tomorrow.
Frequently Asked Questions
How long does the ISO 27001 certification consulting process typically take?
The timeline for achieving certification typically spans six to twelve months. This duration fluctuates based on your organization’s current maturity, the complexity of your digital ecosystem, and the total number of sites in scope. A structured approach ensures that every phase, from initial gap analysis to the final external audit, is executed with precision and thoroughness.
Can a consultant help us transition from ISO 27001:2013 to the 2022 version?
Expert advisors are essential for navigating the transition to the ISO/IEC 27001:2022 standard. Since all previous 2013 certifications expired on October 31, 2025, firms must now align with the updated Annex A controls and the 2024 climate change amendments. Professional ISO 27001 certification consulting provides a clear roadmap to update your ISMS without disrupting existing operations.
What is the difference between an ISO 27001 consultant and an ISO 27001 auditor?
A consultant acts as a strategic architect who builds and implements your management system, while an auditor serves as an independent evaluator. The consultant mentors your team through the complexities of risk management and policy development. Conversely, the auditor verifies that your system meets the standard’s requirements to grant certification. Maintaining this separation is vital to ensure objectivity and avoid conflicts of interest.
Do we need a consultant if we already have an internal IT security team?
Internal IT security teams excel at technical defense, but they often lack the specialized knowledge required for international governance standards. A consultant complements your technical staff by providing the structural framework and documentation expertise needed for a successful audit. This partnership allows your security team to focus on daily operations while the advisor ensures the ISMS aligns with executive business objectives.
How much should we budget for ISO 27001 certification consulting in Canada?
Budgeting for a consulting engagement requires a careful evaluation of your organization’s specific needs and the breadth of your information assets. Total investment depends on factors such as the number of employees, the complexity of your cloud infrastructure, and whether you require an integrated management system. Organizations should prioritize value and long-term sustainability over the lowest initial price to ensure a robust, audit-ready system.
What are the most common mistakes firms make when hiring an ISO 27001 partner?
The most frequent error is selecting a partner that offers a rigid, template-based solution instead of a customized strategy. Firms also struggle when they hire large agencies that assign junior staff to lead complex implementation projects. Success requires a partner who provides senior-level attention and understands how to integrate security into the broader corporate culture and operational workflows.
Does ISO 27001 consulting cover SOC 2 or other security frameworks as well?
While ISO 27001 is a standalone framework, it serves as a foundational “spine” that can be mapped to other standards like SOC 2 or GDPR. Sophisticated ISO 27001 certification consulting utilizes these synergies to reduce administrative redundancy. By building a unified management system, you can satisfy multiple regulatory requirements through a single, cohesive set of controls that protect your digital assets.
How does a consultant help with the Risk Treatment Plan (RTP)?
A consultant transforms your risk assessment into a functional Risk Treatment Plan by identifying the most effective controls for each identified vulnerability. They guide leadership through the strategic decision to treat, transfer, tolerate, or terminate specific risks based on your organization’s risk appetite. This ensures your security investments are proportionate to the actual threats facing your business continuity and digital growth. Organizations looking to build internal audit capability can further strengthen their governance posture by pursuing ISO 27001 lead auditor training to develop in-house expertise that complements external consulting support. Global firms seeking a scalable foundation for resilience can also benefit from exploring professional ISMS implementation services designed to convert compliance requirements into a long-term strategic advantage.
